Regulation (EU) 2024/2847 · Cyber Resilience Act
CRA compliance you can prove.
AnnexProof takes manufacturers of devices and software from risk assessment and SBOM, through 24-hour reporting, to technical documentation with evidence for every Annex I requirement.
§ 01 · Deadlines
The clock is already ticking.
The CRA applies in stages. Reporting has been mandatory since 11 September 2026, including for products placed on the market earlier.
- Entry into force
The transition period starts for manufacturers, importers and distributors.
- Notified bodies
Rules on notifying conformity assessment bodies apply.
- Reporting
Actively exploited vulnerabilities and severe incidents: 24 h, 72 h, final report.
- Full application
Essential requirements, conformity assessment and CE marking.
- Early warning
- 24 hfrom becoming aware
- Notification
- 72 hfull information
- Support period
- 5 yrsat least, as a rule
- Maximum fine
- 2.5%of turnover or EUR 15 m
Articles 13(8), 14, 64(2) and 71 of Regulation (EU) 2024/2847. Fine: the higher of EUR 15 million or 2.5% of total worldwide annual turnover.
Not sure which deadlines apply to your product?
Take the readiness check§ 02 · Article 14
An actively exploited vulnerability. You have 24 hours.
AnnexProof counts the deadlines from the moment you became aware and assembles each package from data already in the system.
since becoming aware
- T+24 hEarly warningProduct, vulnerability, whether it is actively exploited and the Member States where the product is made available.PendingPackage readySubmitted
- T+72 hVulnerability notificationGeneral product information, the nature of the exploit and the vulnerability, corrective measures and advice for users.PendingPackage readySubmitted
- T+14 dFinal reportDescription with severity and impact, plus details of the security update, no later than 14 days after the fix is available.PendingPackage readySubmitted
Article 14(1) and (2) of Regulation (EU) 2024/2847. An authorised person submits the packages via the Single Reporting Platform to the coordinating CSIRT and ENISA.
See what a real CRA case looks like in AnnexProof.
Book a demo§ 03 · Annex I
Requirement. Control. Evidence.
Every essential requirement has a control, and every control has reviewed evidence. Gaps are visible at once.
Annex I coverage
100%Relationship suggestions run locally on rules: no AI model and no data leaves the workspace. A person always decides.
Want to see Annex I coverage for your own product?
Join the programme§ 04 · The app
See what it looks like inside.
Real AnnexProof screens with demo data. The same interface your team will use.
Scroll to browse the screens
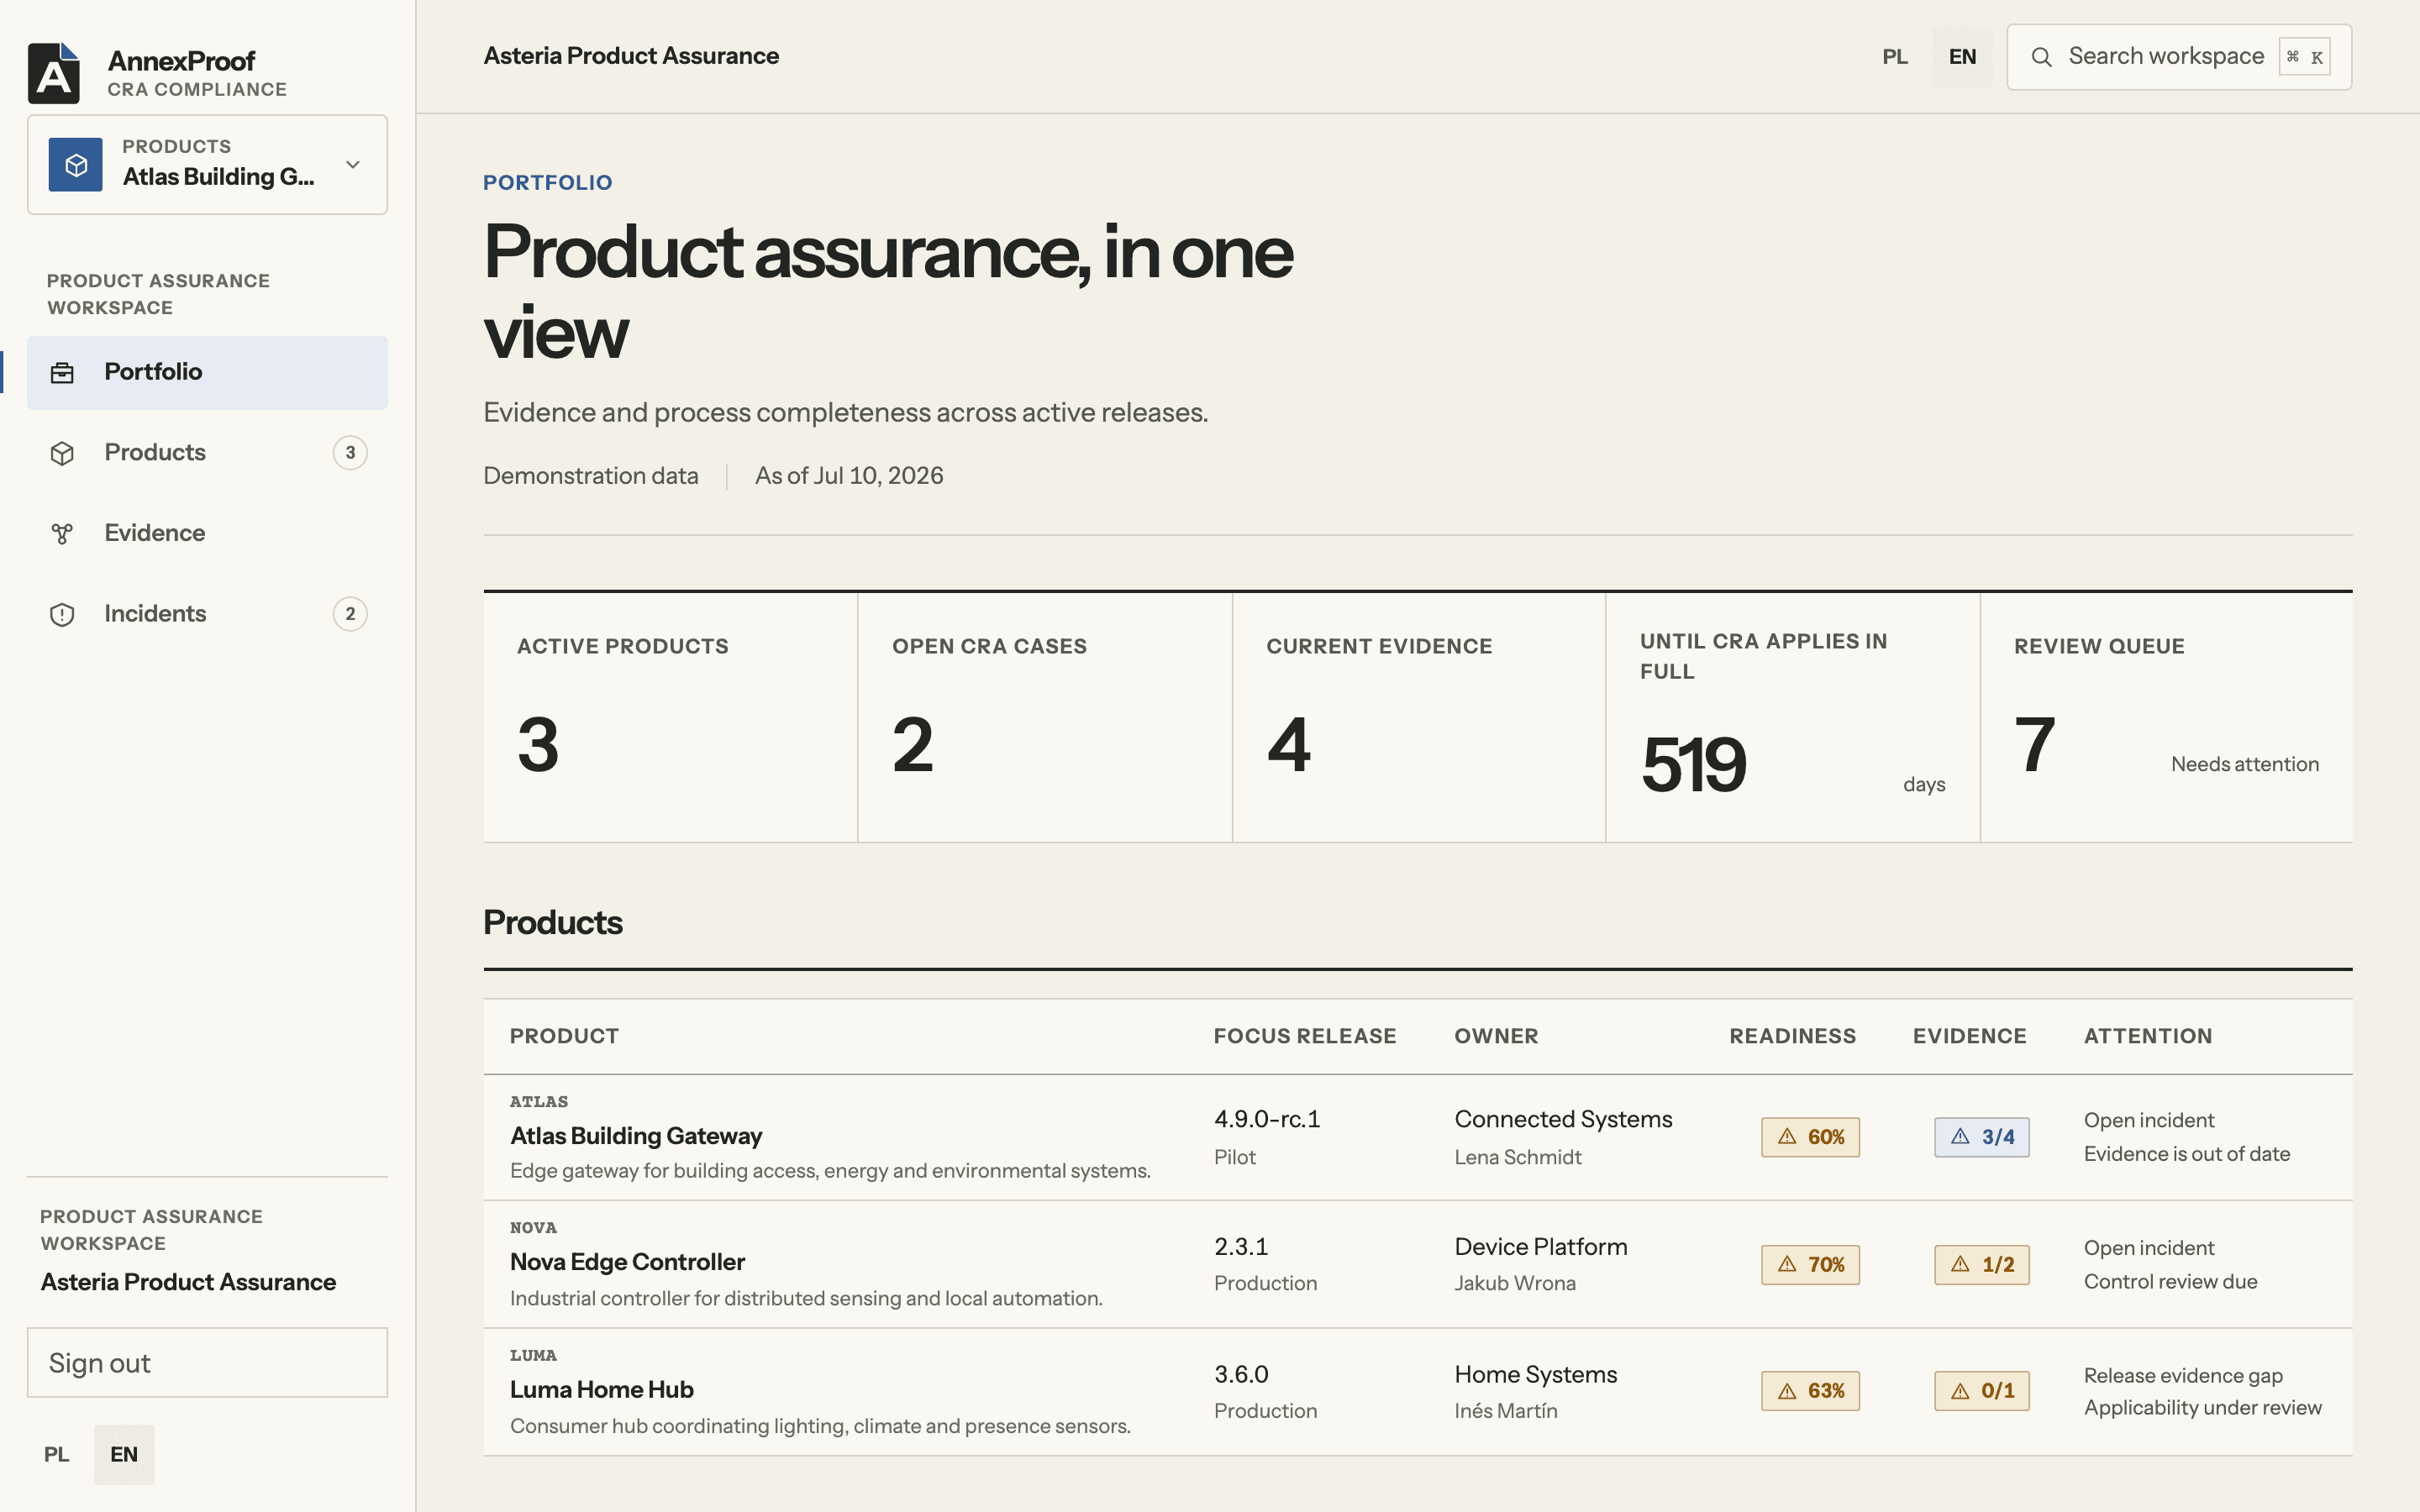 01Portfolio
Every product, open CRA cases and the review queue in one view.
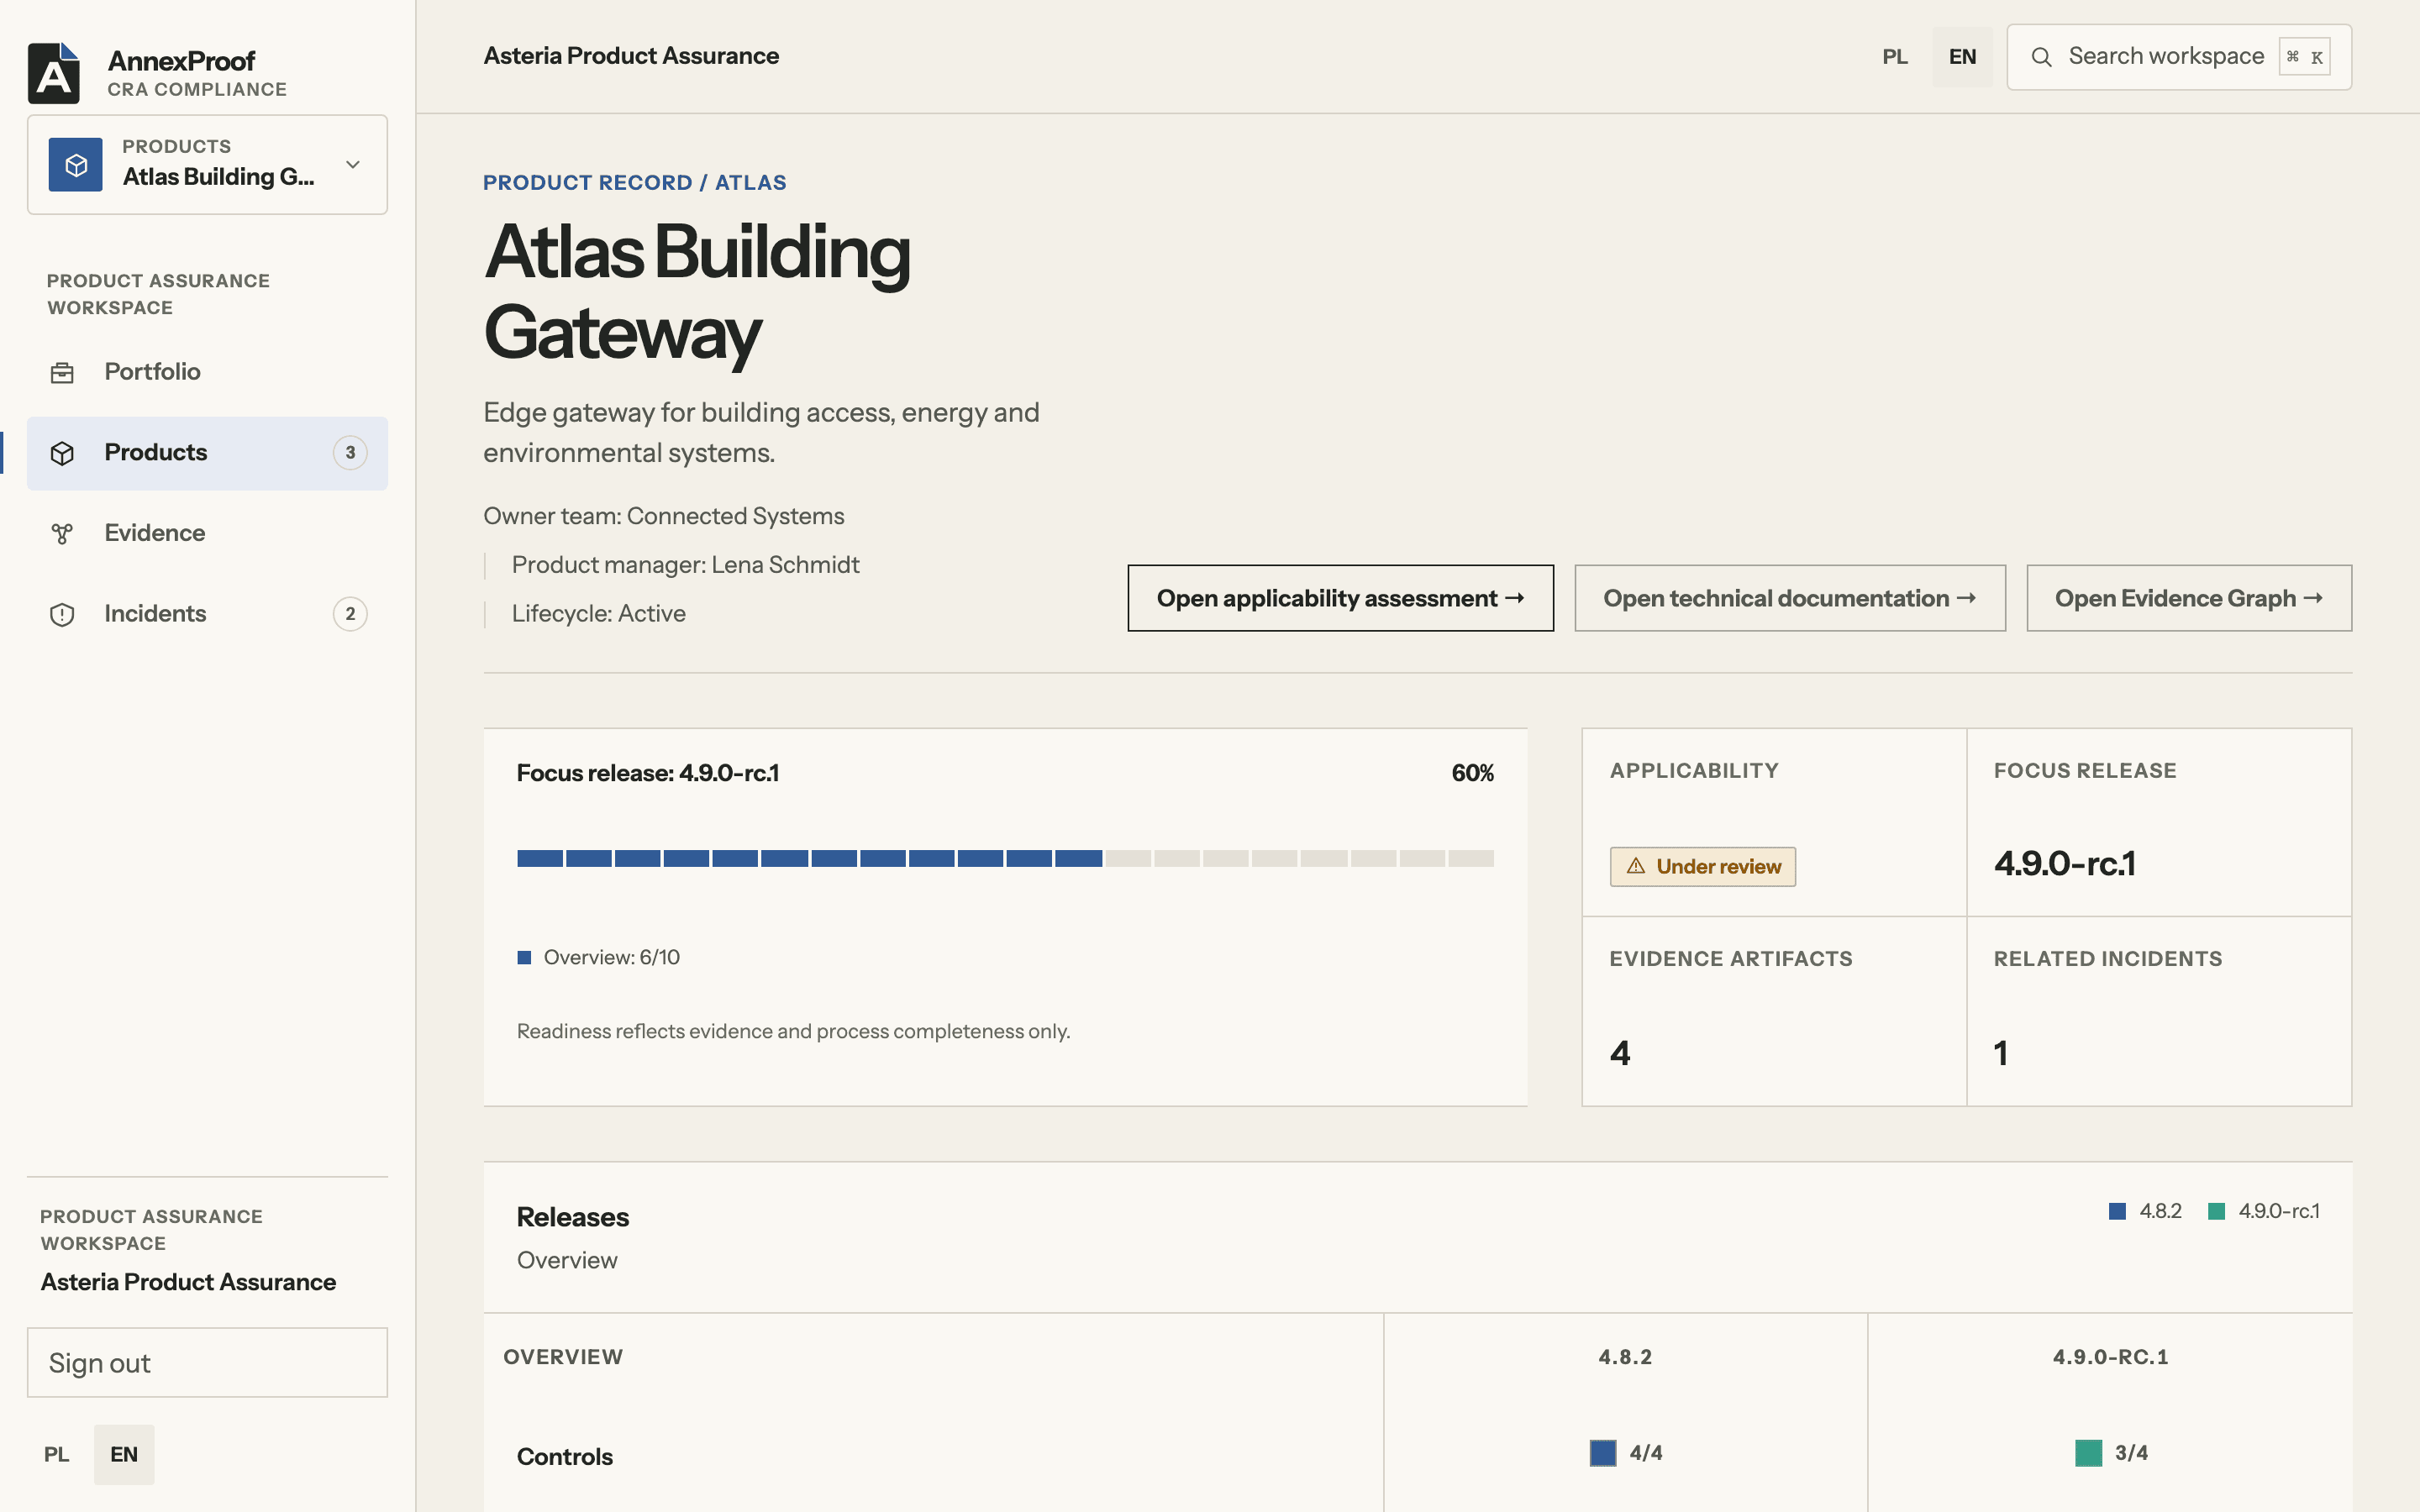 02Product card
Release readiness, CRA applicability, evidence and incidents for a specific version.
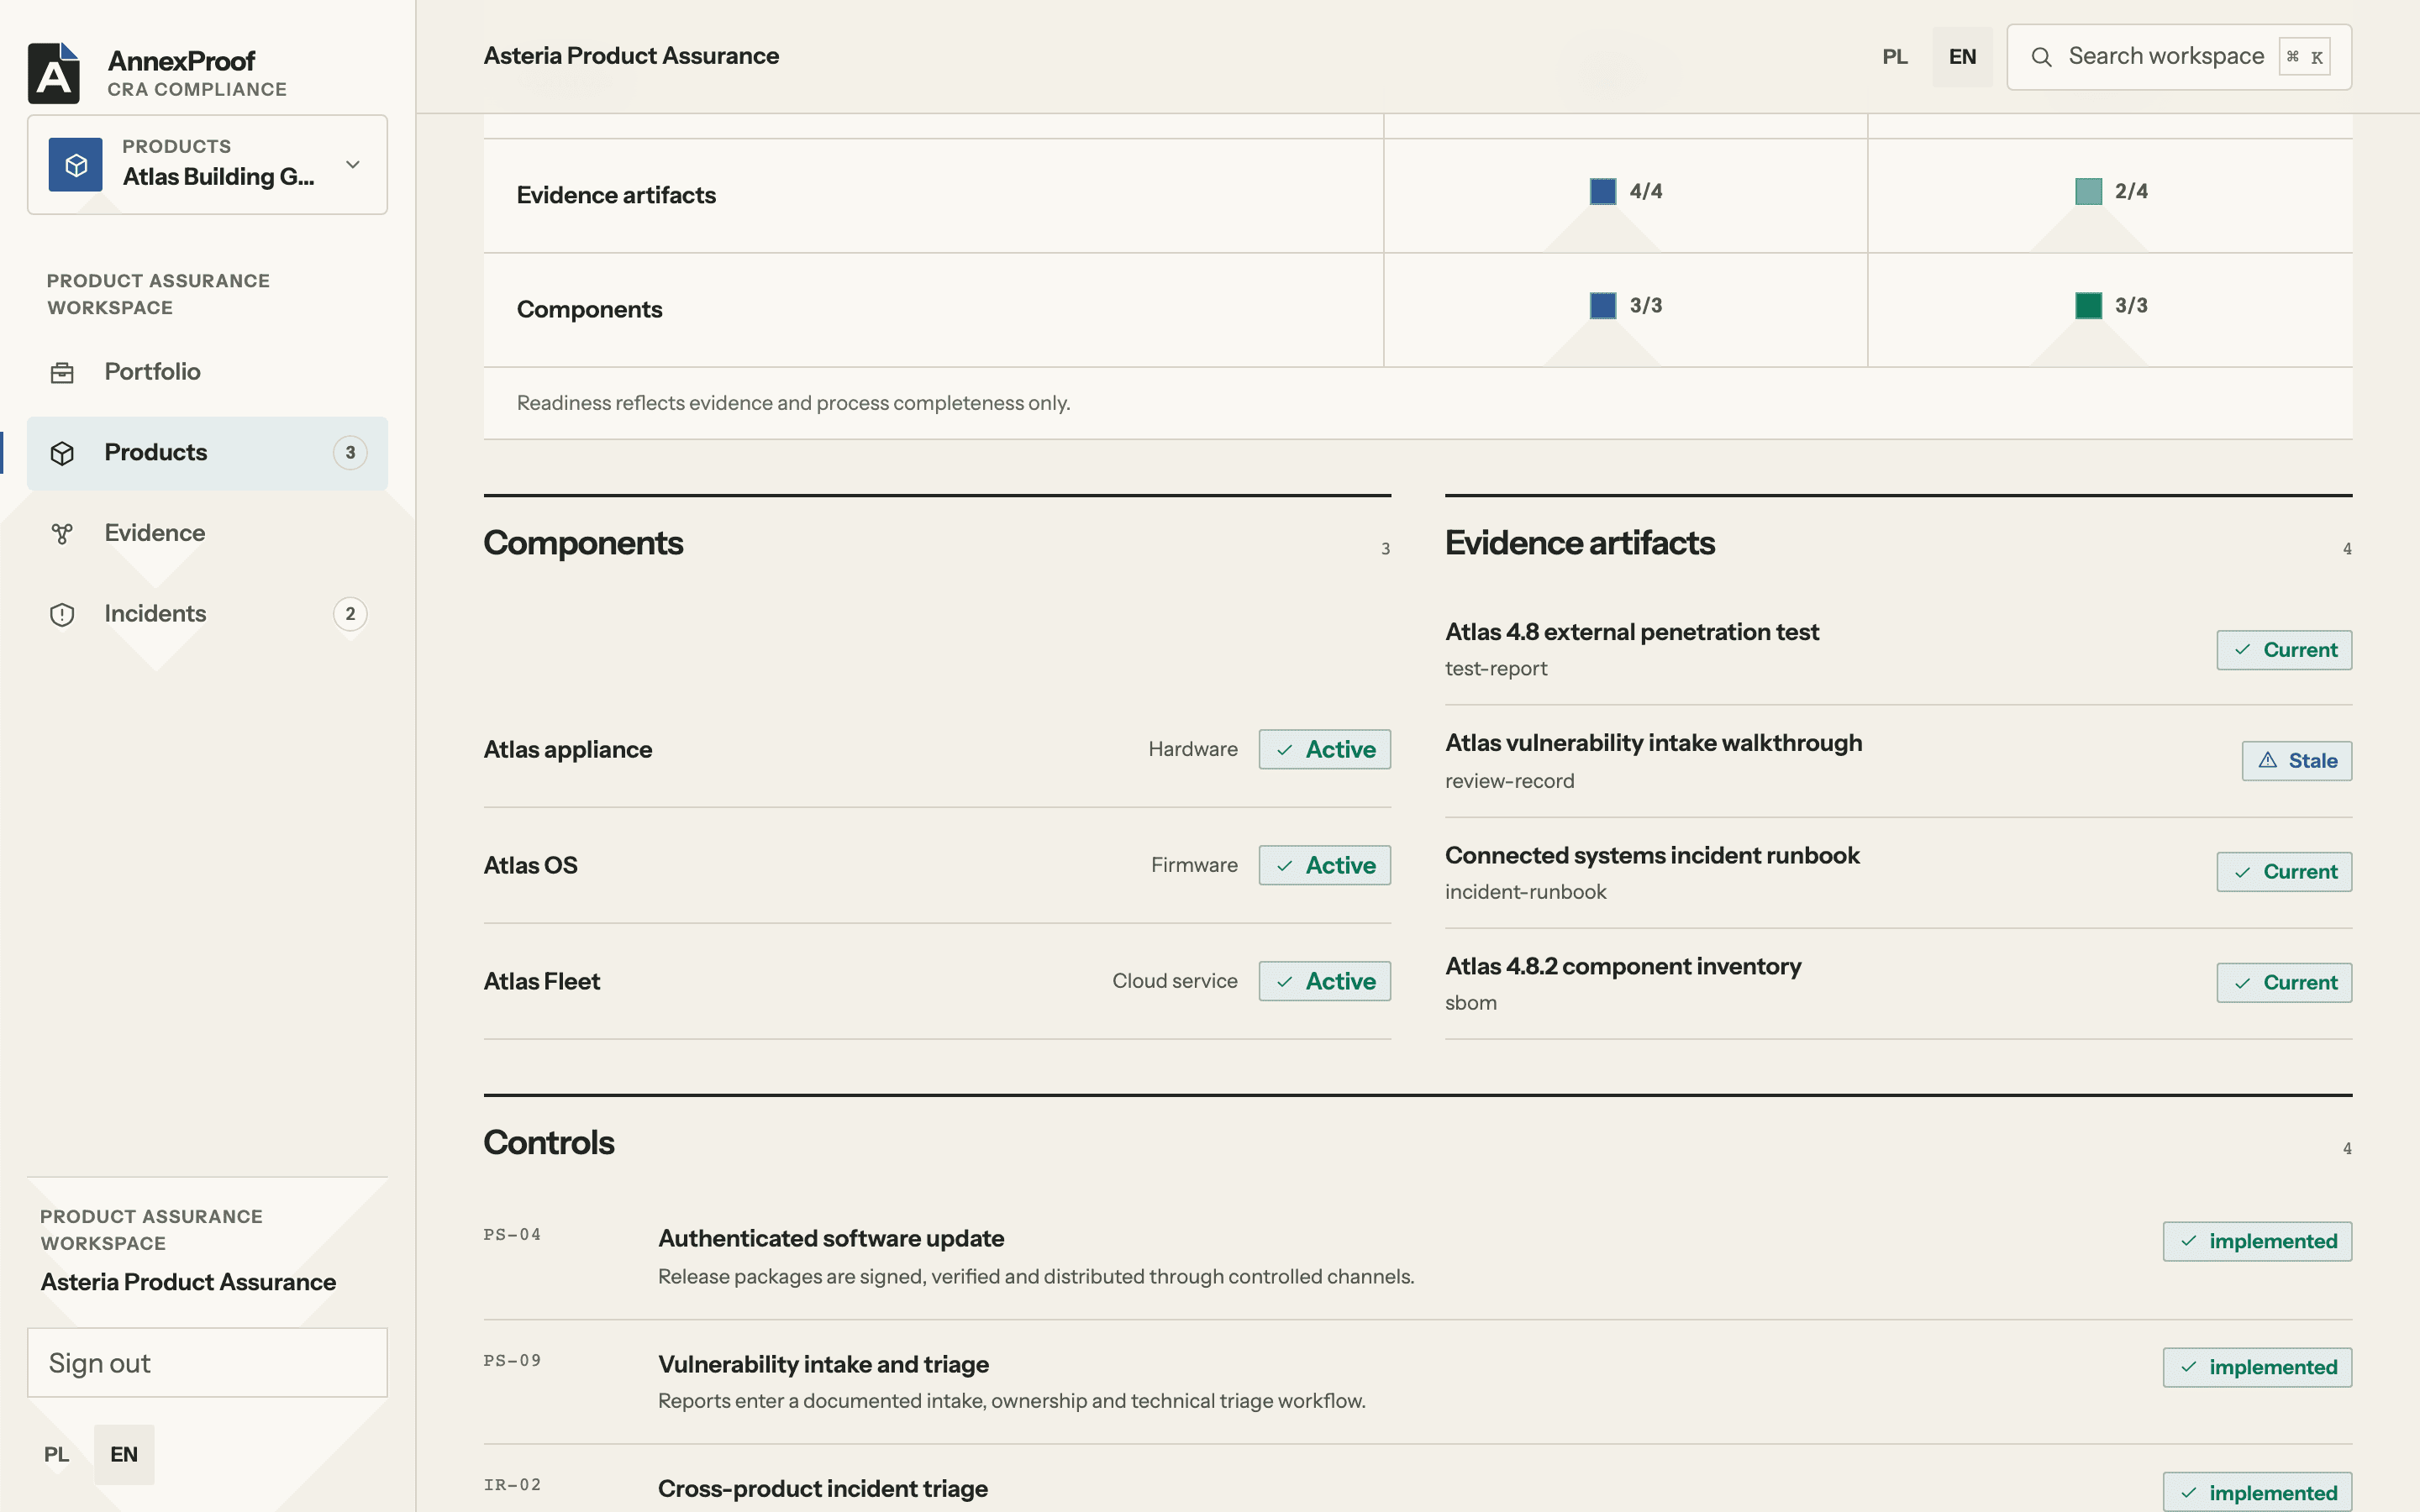 03Release coverage
Components, evidence artefacts and controls, each with its currency status.
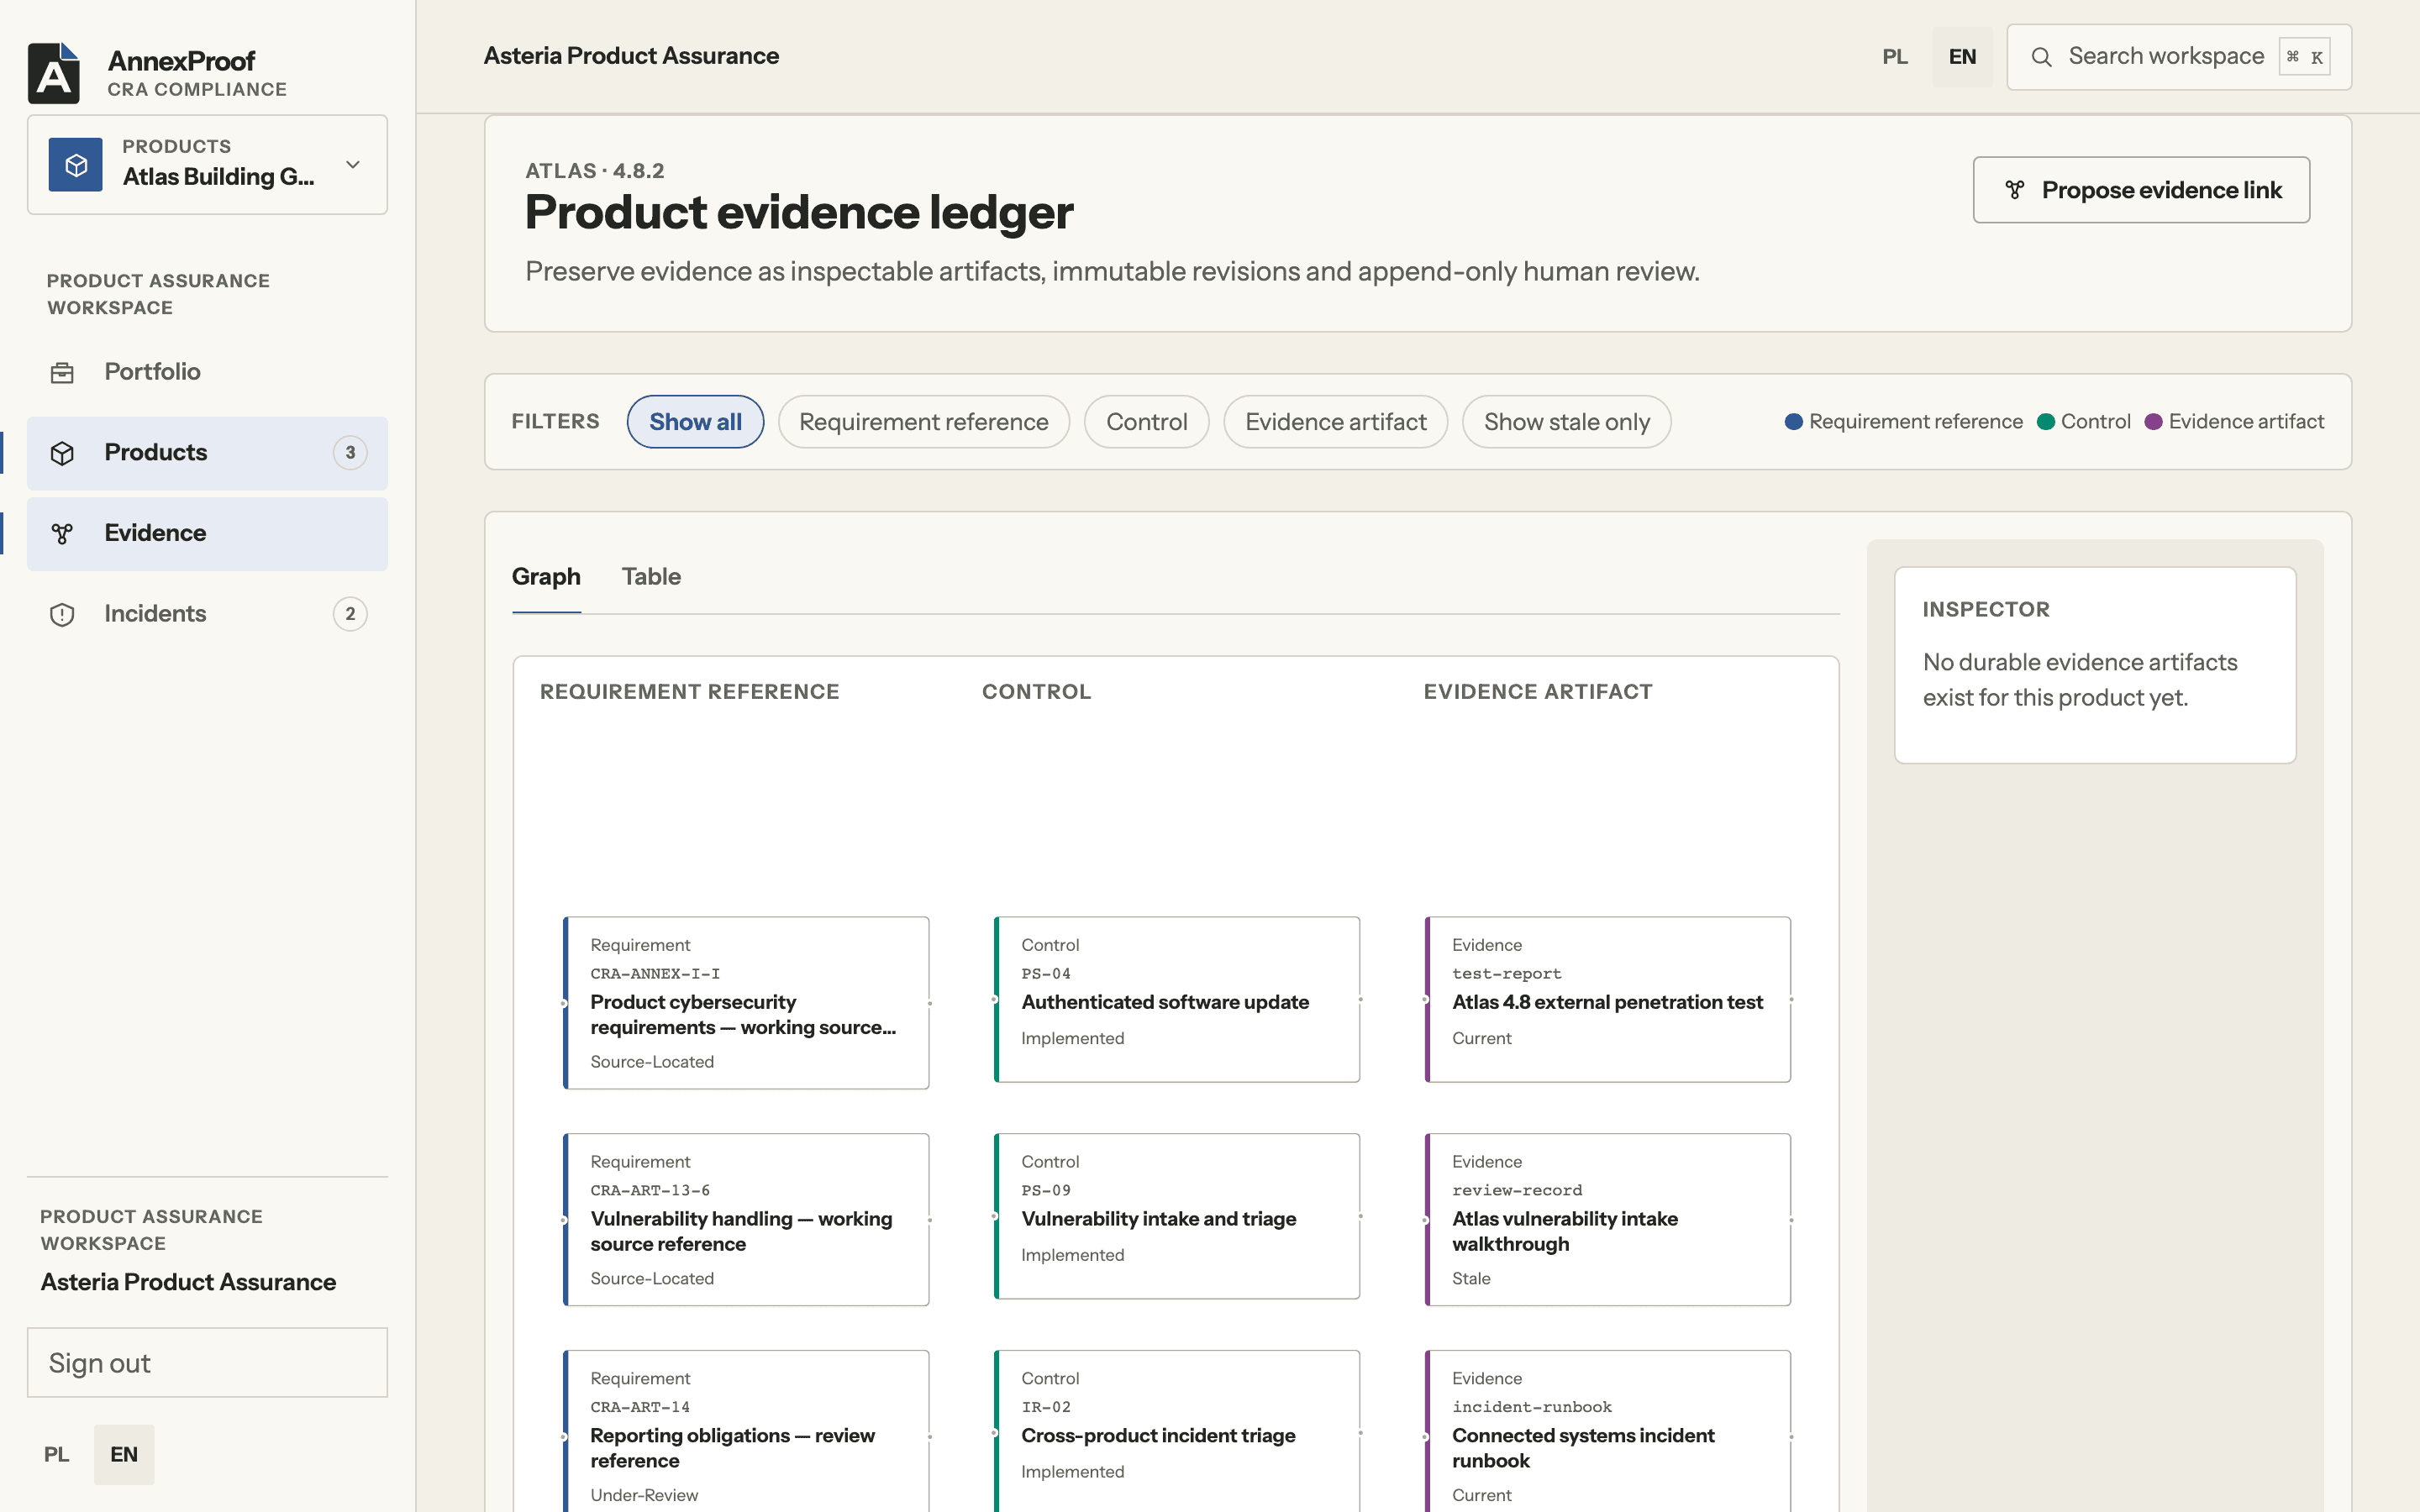 04Evidence register
The requirement → control → evidence graph with immutable revisions and review history.
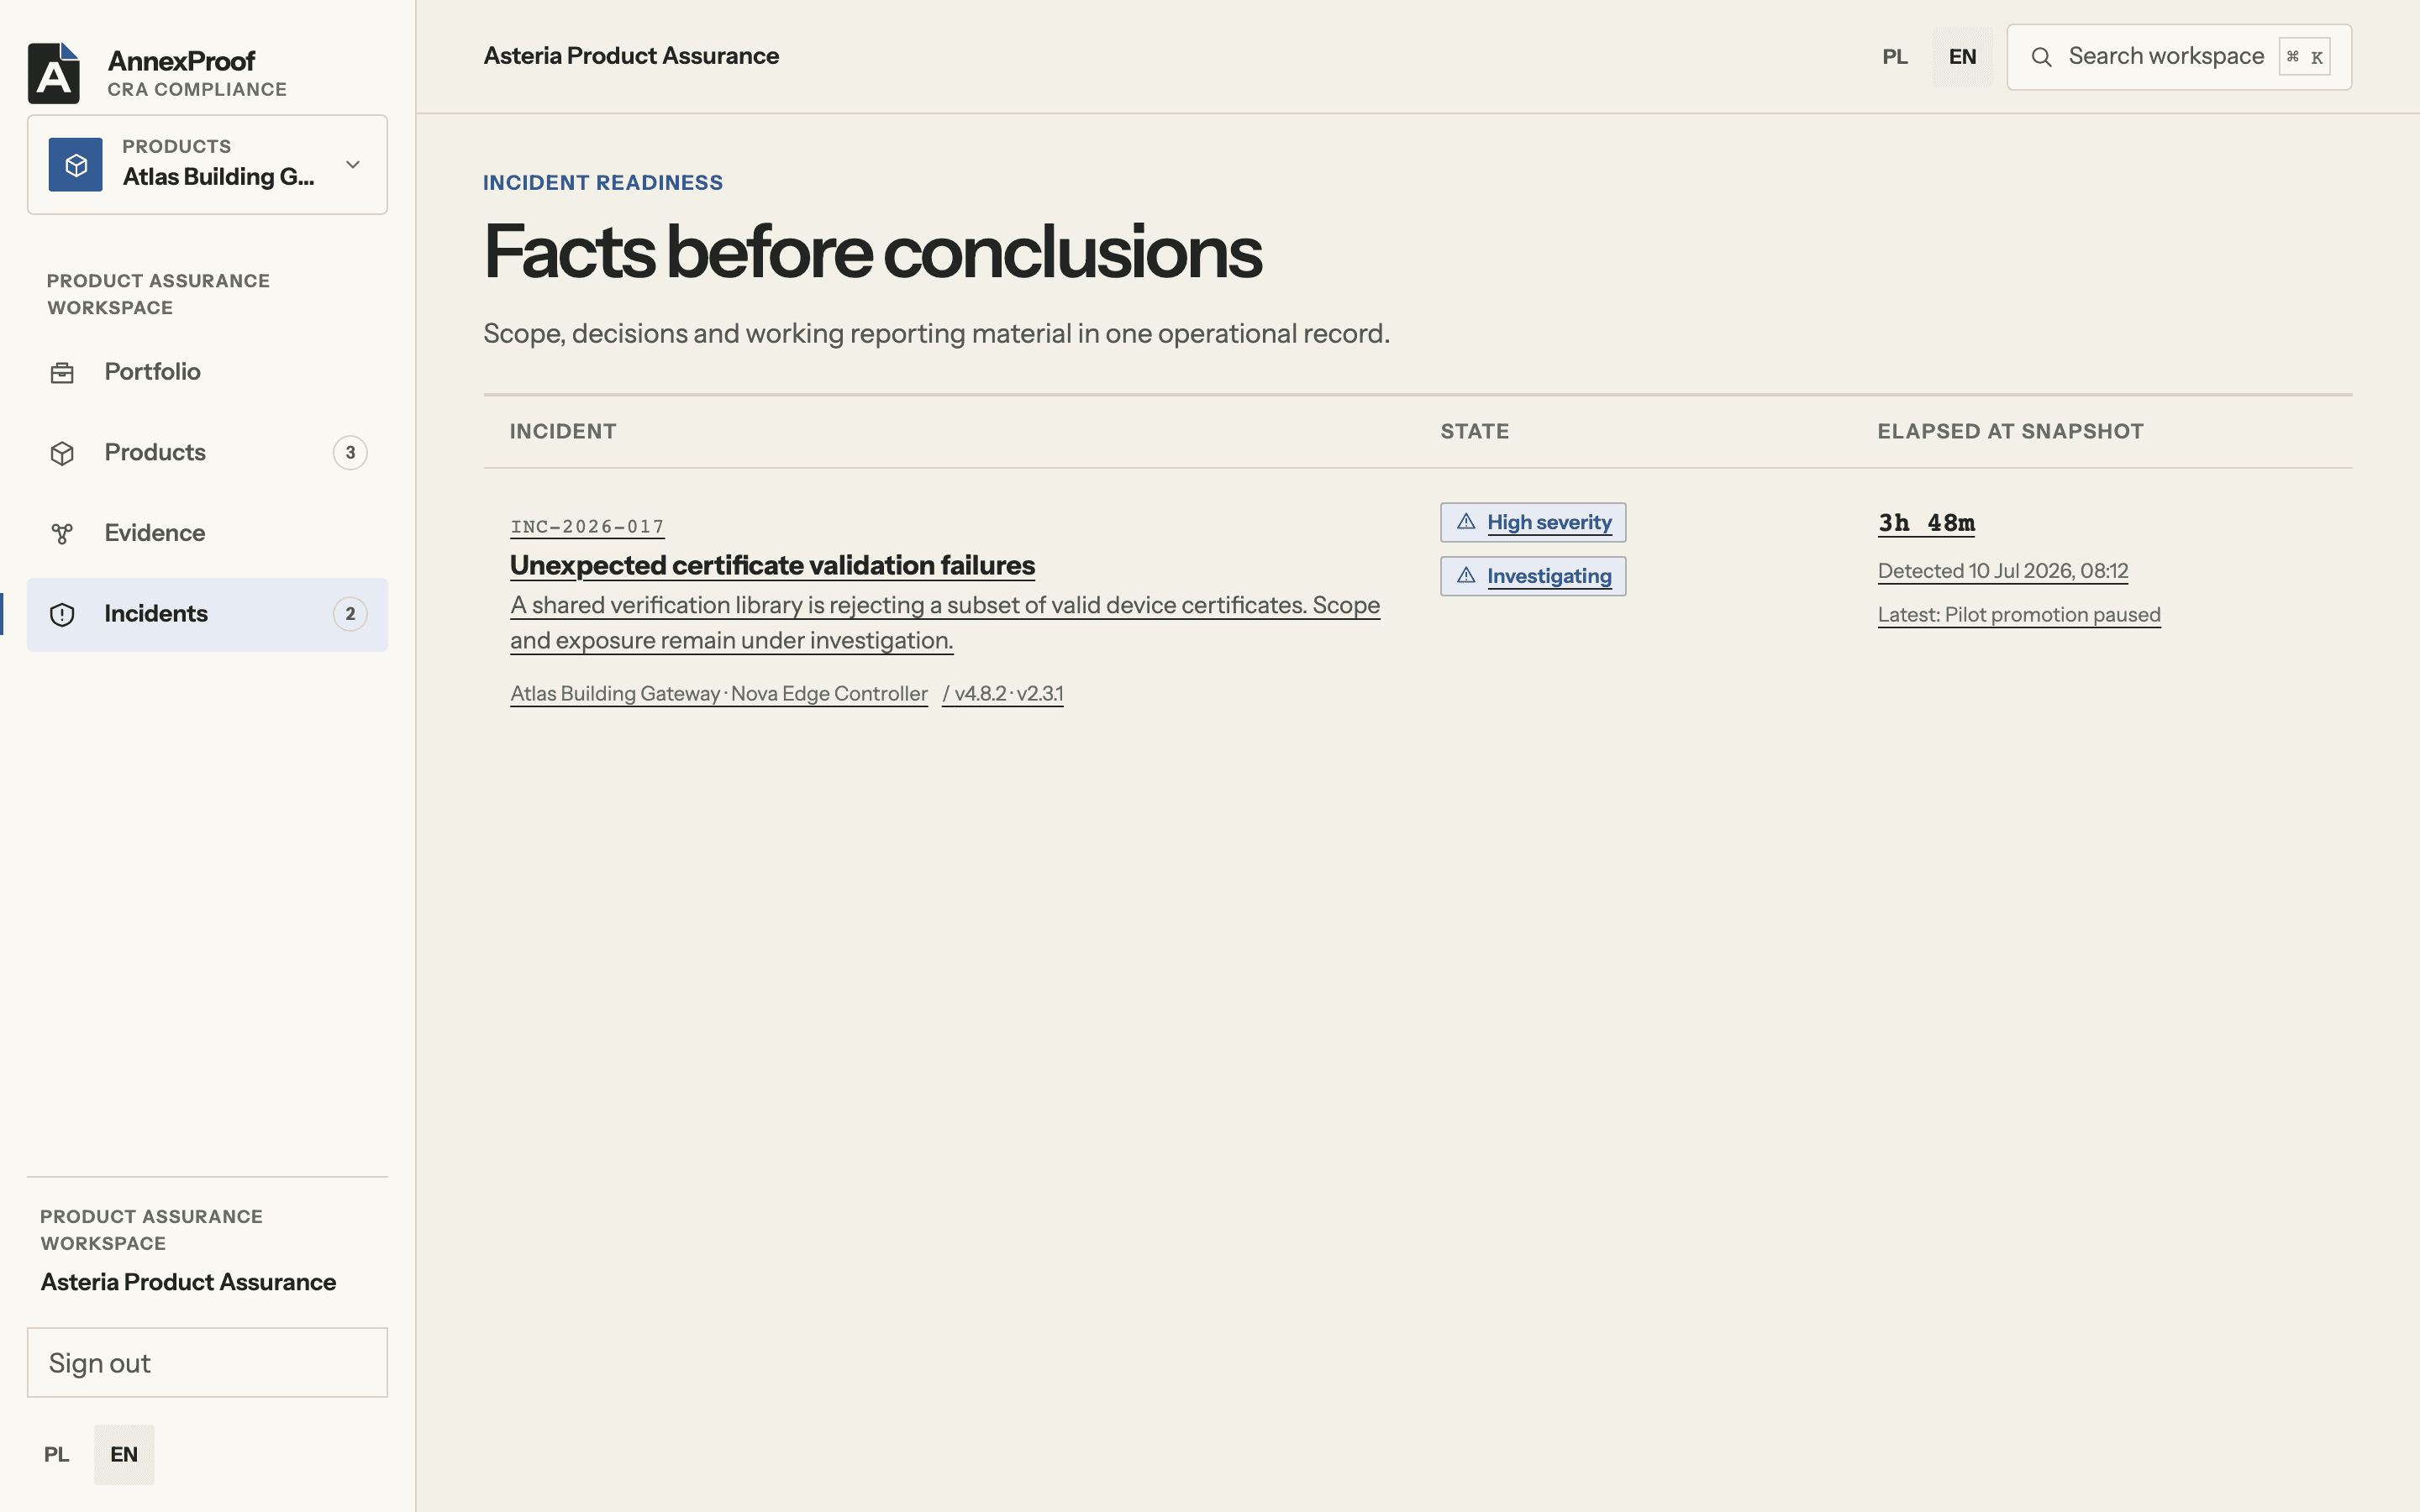 05Incident readiness
Scope, decisions and reporting material in one operational record.
We show the rest live.
CRA cases with deadlines, VEX, the dossier and integrations, on your own product.
Book a demo
§ 05 · SBOM
Every component. Checked every day.
Import CycloneDX and SPDX straight from CI. Daily checks against OSV, CISA KEV and the European ENISA EUVD database, with reasoned VEX decisions.
- pkg:generic/linux@6.12.47Update required
- pkg:generic/busybox@1.36.1Checked
- pkg:generic/openssl@3.0.13VEX decision needed
- pkg:generic/u-boot@2024.01Checked
- pkg:generic/mbedtls@3.6.0VEX: not affected
- pkg:generic/zlib@1.3.1Checked
- pkg:npm/express@4.19.2Checked
- pkg:pypi/cryptography@42.0.5EUVD · under analysis
- pkg:golang/golang.org/x/net@0.24.0Checked
- pkg:cargo/rustls@0.23.5Checked
- pkg:maven/org.eclipse.paho/mqtt@1.2.5VEX: code not reachable
- pkg:npm/ws@8.17.1Checked
Already generate an SBOM in CI? We connect it in the first session.
Book a call§ 06 · Modules
The whole CRA process in one place.
From deciding whether the CRA applies at all to a documentation snapshot for every release.
- 01ApplicabilityApplicability and classificationWhether and how the CRA applies: category, support period and conformity assessment route, with a rationale.
- 02RiskProduct models and risk assessmentArchitecture, data, interfaces and a risk model mapped to the essential requirements, with treatment decisions.
- 03EvidenceEvidence graph and Evidence VaultVersioned, reviewed evidence, relationship suggestions and a hash-chained audit log.
- 04VulnerabilitiesSBOM, monitoring and VEXCycloneDX and SPDX import, daily component checks and status export as CSAF 2.0 or CycloneDX VEX.
- 05Art. 14CRA cases and reportingReportability assessment, 24 h / 72 h / 14-day deadlines, reminders and ready packages.
- 06CVDCoordinated disclosureA public report form for researchers, a CVD policy and security.txt for every workspace.
- 07DossierTechnical documentationA dossier compiled from accepted data, with review, acceptance and a downloadable snapshot of every release.
Don’t wait for the first incident.
Reporting is already mandatory. Check where you stand in 3 minutes, or let’s talk about your product.
§ 07 · Readiness check
Where are you with the CRA?
10 questions, 3 minutes. You see your score and the biggest gaps right away. No email required.
§ 08 · Design partners
Five places. We take your first product through together.
We are looking for manufacturers of devices and software who want to get through the CRA now and shape the product.
- Places in the programme
- 5
- Product end to end
- 1from applicability to dossier
- Feedback
- 30 minevery two weeks
What you get
- Onboarding led personally by the founder
- Your first product taken through the whole process
- Preferential launch terms
- Direct influence on the roadmap
What we ask
- Regular feedback
- A case study after rollout (can be anonymous)
§ 09 · Questions
Frequently asked questions
01Does the CRA apply to my company?
The CRA covers manufacturers, importers and distributors of products with digital elements made available on the EU market: from IoT devices and network equipment to software sold as a product. Medical devices and vehicles covered by their own rules are among the exclusions. The readiness check gives a first indication.
02Does AnnexProof replace a lawyer or a notified body?
No. AnnexProof organises the work and the evidence, tracks deadlines and generates documentation. Legal decisions and third-party assessment stay with the people and bodies responsible for them.
03Does AnnexProof submit reports to ENISA for me?
It prepares complete 24-hour, 72-hour and final packages and tracks the deadlines. The submission via the Single Reporting Platform is done by an authorised person in your company.
04We already have an SBOM and a vulnerability scanner. Why AnnexProof?
A scanner tells you what is vulnerable. The CRA asks for more: reasoned decisions, reporting deadlines, VEX, documentation and evidence for every requirement. AnnexProof takes the data from your tools and turns it into compliance.
05Where is the data stored?
In the European Union. Access is protected by multi-factor authentication, and each organisation’s data is isolated from the others.
06Can I export my data?
Yes. SBOM, VEX, documentation and release snapshots can be downloaded, and key data is also available through the REST API.
07How much does it cost?
We are setting pricing together with our first customers in the design partner programme. Let us talk about your scale: number of products and releases per year.
§ 10 · Contact
Let’s talk about your product.
30 minutes: we go through your product, the CRA deadlines and the biggest gaps. No commitment.
Or write tokontakt@annexproof.com